The era of the nation-state operator patiently typing at a keyboard is quietly ending. Microsoft says a China-aligned group it tracks as Storm-0940 ran a large-scale supply chain campaign through the compromised ConnectWise Cloud Backup application — and handed much of the work to autonomous AI agents, according to The Register, which covered Microsoft's research write-up.
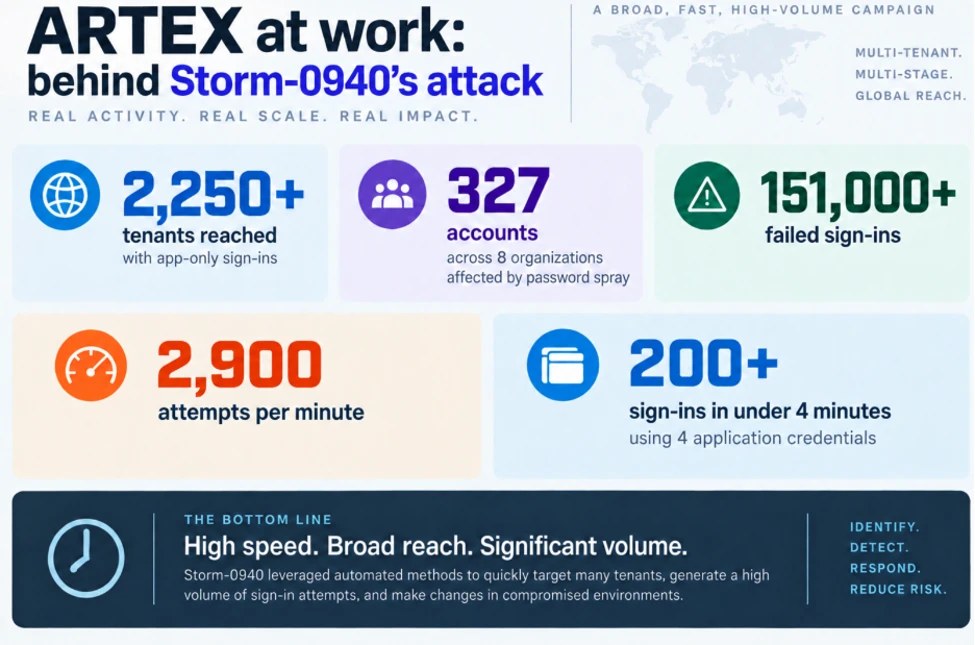
The tool was ARTEX, an open-source penetration-testing framework written in Go that chains LLM-driven agents into an end-to-end attack: reconnaissance, vulnerability discovery, credential attacks, data theft. Microsoft says Storm-0940 started using it as early as September against organizations spanning aerospace and defense, government, energy, semiconductors, and tech. After gaining control of ConnectWise cloud application identities, the agents authenticated to downstream Microsoft 365 tenants using trust those tenants had already granted — no interactive login required — and in multiple cases went from initial targeting to privileged cloud access in less than three hours. At peak intensity the campaign hit 2,900 sign-in attempts per minute across more than 2,250 tenants.
There are two genuinely new things here, and both should worry defenders. First, the speed collapse: Microsoft notes the alerts fired, but three hours from target selection to domain-level access doesn't leave time for a human SOC workflow to triage, confirm, and remediate before the damage is done. Second, the backdoor problem: Storm-0940's agents modified application credentials and privilege assignments inside victim tenants, meaning the attacker's access can survive the cleanup of the original compromised ConnectWise identities. Microsoft is pointedly telling customers not to just delete the enterprise applications as a first response — preserve the evidence first, or you'll never know what else the agents touched.
The uncomfortable part is provenance. ARTEX is a legitimate, freely available tool, and Microsoft has already spotted actors in several regions using it; it was previously abused in breaches of South Korean financial institutions. The same multi-agent frameworks security teams are buying to run automated red-teaming are now the nation-state's scale multiplier. This is the pattern the AI-safety community has been warning about in the abstract: not some exotic novel exploit, but ordinary credential theft executed at machine speed by software nobody has to license, restrict, or export-control. You can't sanction an open-source GitHub repo.
ConnectWise — which shut down its Cloud Backup, SaaS Security, and Cloud Management services after discovering the unauthorized access, and which took a similar hit via ScreenConnect last year — says it has contained the affected application connections. But containment of the supply chain doesn't undo the persistence the agents may have planted downstream. Every organization whose Microsoft 365 tenant ever trusted a high-privilege third-party OAuth app should be auditing right now, because the thing that got breached wasn't really ConnectWise. It was the trust model.
— via The Register